
AZ-140 · Question #204
Your on-premises network contains an Active Directory Domain Services (AD DS) domain named contoso.com. You have an Azure subscription that is linked to a Microsoft Entra tenant named…
The correct answer is A. User1 only. Only User1 will be able to sign in to the Azure Virtual Desktop session hosts because the hosts are joined to the on-premises contoso.com domain, and User1 is the only one who can authenticate against that domain.
Question
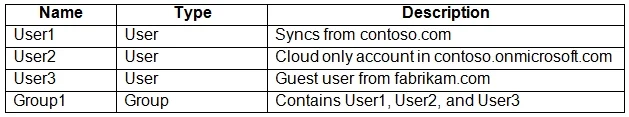
Your on-premises network contains an Active Directory Domain Services (AD DS) domain named contoso.com. You have an Azure subscription that is linked to a Microsoft Entra tenant named contoso.onmicrosoft.com. Contoso.com syncs with contoso.onmicrosoft.com. You have a partner company that has a Microsoft Entra tenant named fabrikam.com. Contoso.onmicrosoft.com contains the resources shown in the following table. You deploy an Azure Virtual Desktop host pool named Pool1. Pool1 contains 10 session hosts that are joined to Contoso.com. You assign Group1 to the application group in Pool1. You need to identify which users will be able to sign in to the session hosts in Pool1. Which users should you identify?
Exhibit
Options
- AUser1 only
- BUser1 and User2 only
- CUser1 and User3 only
- DUser1, User2, and User3
How the community answered
(23 responses)- A70% (16)
- B17% (4)
- C9% (2)
- D4% (1)
Why each option
Only User1 will be able to sign in to the Azure Virtual Desktop session hosts because the hosts are joined to the on-premises contoso.com domain, and User1 is the only one who can authenticate against that domain.
The Azure Virtual Desktop session hosts are joined to the on-premises Active Directory Domain Services (AD DS) domain contoso.com. Only User1, who originates from and is synced from contoso.com AD DS, can authenticate against the domain-joined session hosts. User1 is also a member of Group1, which is assigned to the application group, granting authorization.
User2 is a cloud-only user in contoso.onmicrosoft.com and does not exist in or cannot authenticate directly against the on-premises contoso.com AD DS domain to which the session hosts are joined.
User3 is from a partner Microsoft Entra tenant (fabrikam.com) and cannot authenticate against the on-premises contoso.com AD DS domain where the session hosts are joined.
Both User2 and User3 cannot authenticate against the on-premises contoso.com domain that the session hosts are joined to, making this choice incorrect.
Concept tested: Azure Virtual Desktop authentication with on-premises AD DS
Source: https://learn.microsoft.com/en-us/azure/virtual-desktop/overview-identity
Topics
Community Discussion
No community discussion yet for this question.