
AI-102 · Question #88
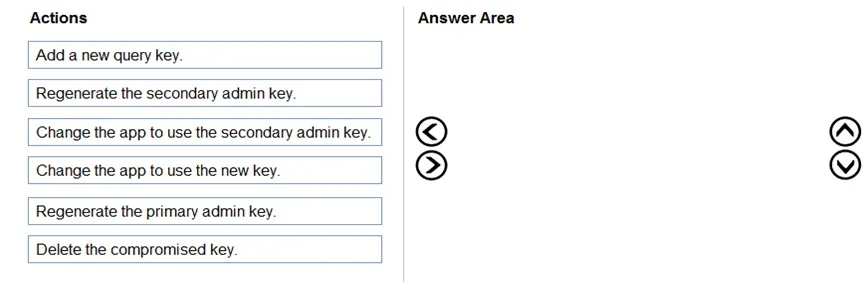
Drag and Drop Question You have a web app that uses Azure AI Search. When reviewing billing for the app, you discover much higher than expected charges. You suspect that the query key is…
The correct answer is Add a new query key.; Change the app to use the new key.; Delete the compromised key. The correct sequence creates a new query key first, then updates the app to use it (minimizing downtime by ensuring the app never loses access), and finally deletes the compromised key to revoke unauthorized access. Query keys provide read-only access to the documents…
Question
Exhibit
Answer Area
Drag items
Correct arrangement
- Add a new query key.
- Change the app to use the new key.
- Delete the compromised key.
Explanation
The correct sequence creates a new query key first, then updates the app to use it (minimizing downtime by ensuring the app never loses access), and finally deletes the compromised key to revoke unauthorized access. Query keys provide read-only access to the documents collection by design, which satisfies the requirement without granting excessive admin-level permissions. This approach ensures zero-downtime rotation because the app is always authenticated before the old key is invalidated.
Topics
Community Discussion
No community discussion yet for this question.