
350-601 · Question #158
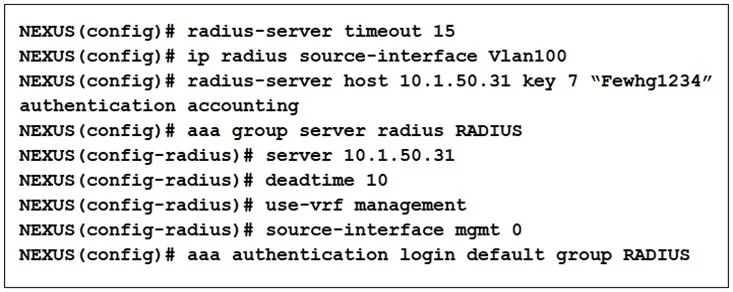
Refer to the exhibit. What is the result of implementing the configuration?
The correct answer is C. Only the RADIUS server is used for authentication. The exhibit shows a RADIUS configuration where the AAA (Authentication, Authorization, and Accounting) settings specify RADIUS as the authentication method without a local fallback (e.g., 'aaa authentication login default group radius' with no 'local' keyword appended). This…
Question
Refer to the exhibit. What is the result of implementing the configuration?
Exhibit
Options
- ARADIUS traffic is sourced from the VLAN 200 interface.
- BThe RADIUS server timeout value is 15 milliseconds.
- COnly the RADIUS server is used for authentication.
- DUsers specify the RADIUS server when they log in.
How the community answered
(26 responses)- A8% (2)
- B4% (1)
- C88% (23)
Explanation
The exhibit shows a RADIUS configuration where the AAA (Authentication, Authorization, and Accounting) settings specify RADIUS as the authentication method without a local fallback (e.g., 'aaa authentication login default group radius' with no 'local' keyword appended). This means only the RADIUS server will be used for authentication - if the RADIUS server is unreachable, authentication will fail entirely rather than falling back to local credentials. The source interface specified is for RADIUS packets (not necessarily VLAN 200 - A is incorrect). The timeout value is in seconds, not milliseconds (B is incorrect). Users do not manually select the RADIUS server at login (D is incorrect); the server group is configured administratively.
Topics
Community Discussion
No community discussion yet for this question.