
350-501 · Question #185
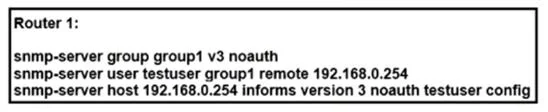
Refer to the exhibit. A network engineer is deploying SNMP configuration on client's routers. Encrypted authentication must be included on router 1 to provide security and protect message…
The correct answer is B. snmp-server user testuser group 1 remote 192.168.0.254 v3 auth md5 testpassword. To configure SNMPv3 with encrypted authentication and message confidentiality, the engineer must define an SNMPv3 user with authentication and privacy parameters.
Question
Refer to the exhibit. A network engineer is deploying SNMP configuration on client's routers. Encrypted authentication must be included on router 1 to provide security and protect message confidentially. Which action should the engineer perform on the routers to accomplish this task?
Exhibit
Options
- Asnmp-server host 192.168.0.254 informs version 3 auth testuser config.
- Bsnmp-server user testuser group 1 remote 192.168.0.254 v3 auth md5 testpassword
- Csnmp-server group group 1 v3 auth.
- Dsnmp-server community public
How the community answered
(49 responses)- A2% (1)
- B84% (41)
- C4% (2)
- D10% (5)
Why each option
To configure SNMPv3 with encrypted authentication and message confidentiality, the engineer must define an SNMPv3 user with authentication and privacy parameters.
The `snmp-server host` command is used to specify the NMS host to which traps/informs are sent and refers to a pre-configured user for authentication, it does not configure the user's authentication or confidentiality parameters on the router itself.
The `snmp-server user` command is used to configure an SNMPv3 user. By including `v3 auth md5 testpassword`, the engineer is enabling authentication for the user `testuser` using the MD5 protocol and a specified password, which is a necessary step for encrypted authentication in SNMPv3. To additionally provide message confidentiality, the `priv` keyword with a privacy protocol (e.g., `des` or `aes`) and its password would also need to be specified in this command.
The `snmp-server group` command defines an SNMPv3 group and its security model, but it does not define individual users, their authentication details, or confidentiality settings, which are crucial for the problem's requirements.
`snmp-server community public` configures an SNMPv1/v2c community string, which provides no encryption for authentication or message confidentiality, directly contradicting the requirement for 'encrypted authentication' and 'message confidentiality.'
Concept tested: SNMPv3 user configuration for authentication and privacy
Source: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/snmp/configuration/xe-16-10/snmp-xe-16-10-book/snmpv3-configuration.html
Topics
Community Discussion
No community discussion yet for this question.