
312-50V10 · Question #627
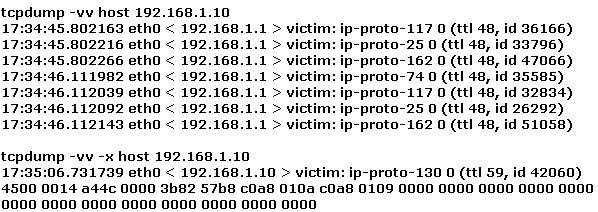
Study the log below and identify the scan type.
The correct answer is D. nmap -sO -T 192.168.1.10. The scan log reflects an IP protocol scan with a timing template, matching nmap -sO -T.
Question
Study the log below and identify the scan type.
Exhibit
Options
- Anmap -sR 192.168.1.10
- Bnmap -sS 192.168.1.10
- Cnmap -sV 192.168.1.10
- Dnmap -sO -T 192.168.1.10
How the community answered
(59 responses)- A7% (4)
- B12% (7)
- C27% (16)
- D54% (32)
Why each option
The scan log reflects an IP protocol scan with a timing template, matching nmap -sO -T.
The -sR flag performs an RPC scan that enumerates RPC program numbers on open portmapper/rpcbind ports, producing output with RPC program names rather than raw protocol numbers.
The -sS flag performs a TCP SYN stealth scan targeting only TCP ports, producing a log of TCP port states (open/closed/filtered) rather than IP protocol enumeration.
The -sV flag performs service and version detection on already-identified open ports, producing output with service banners and version strings rather than protocol scan results.
The -sO flag directs nmap to perform an IP protocol scan, which cycles through IP protocol numbers (not TCP/UDP port numbers) to determine which layer-3 protocols the target supports - producing log entries listing protocol IDs rather than port states. The -T flag sets a timing template to control scan speed, and this combination produces the distinctive log pattern shown.
Concept tested: Nmap IP protocol scan (-sO) identification
Source: https://nmap.org/book/man-port-scanning-techniques.html
Topics
Community Discussion
No community discussion yet for this question.