
300-715 · Question #219
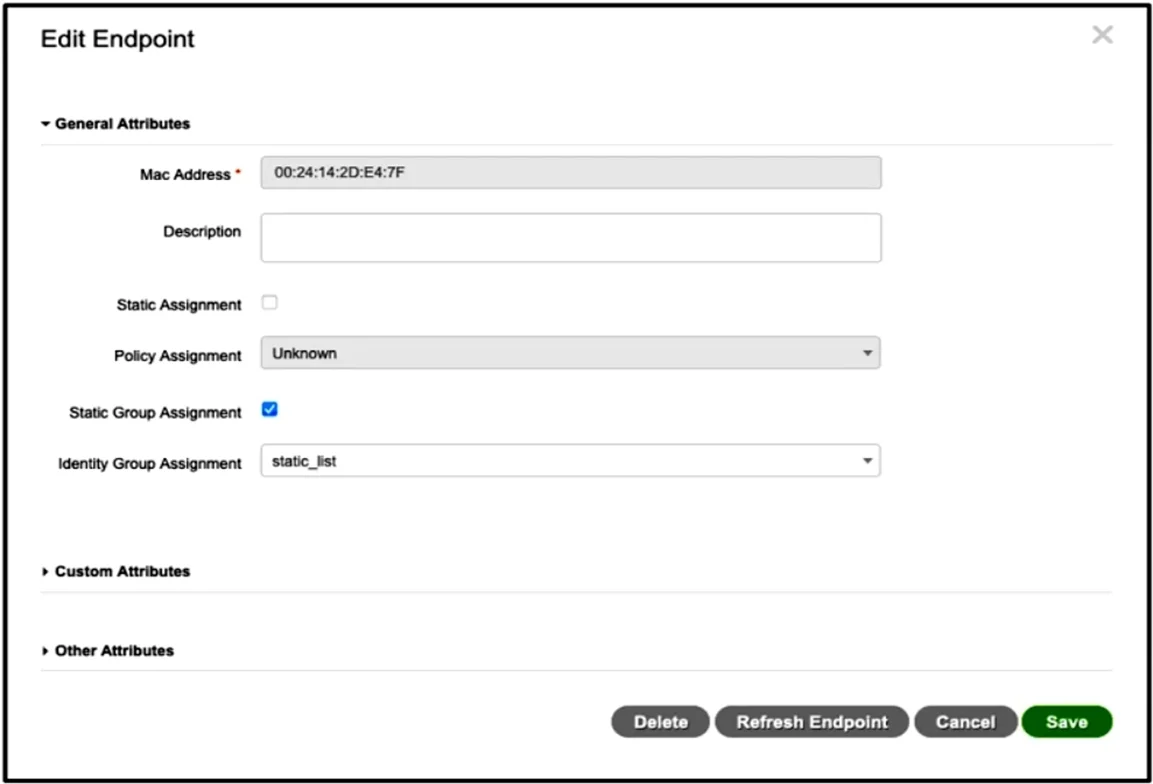
Refer to the exhibit. An administrator is manually adding a device to a Cisco ISE identity group to ensure that it is able to access the network when needed without authentication. Upon testing, the…
The correct answer is C. The logical profile is being statically assigned instead of the identity group. The authorization policy fails to match because it checks for a LogicalProfile, but the administrator mistakenly assigned the device to an Identity Group, which are distinct classification attributes in Cisco ISE.
Question
Refer to the exhibit. An administrator is manually adding a device to a Cisco ISE identity group to ensure that it is able to access the network when needed without authentication. Upon testing, the administrator notices that the device never hits the correct authorization policy line using the condition EndPoints LogicalProfile EQUALS static_list. Why is this occurring?
Exhibit
Options
- AThe dynamic logical profile is overriding the statically assigned profile
- BThe device is changing identity groups after profiling instead ot remaining static
- CThe logical profile is being statically assigned instead of the identity group
- DThe identity group is being assigned instead of the logical profile
How the community answered
(28 responses)- A7% (2)
- B18% (5)
- C71% (20)
- D4% (1)
Why each option
The authorization policy fails to match because it checks for a `LogicalProfile`, but the administrator mistakenly assigned the device to an `Identity Group`, which are distinct classification attributes in Cisco ISE.
There is no indication that a dynamic logical profile is overriding a static one; the core issue is a mismatch between the policy's expectation and the configuration action.
The authorization policy condition `EndPoints LogicalProfile EQUALS static_list` explicitly looks for a specific logical profile. However, the administrator manually added the device to an *identity group*. Since logical profiles and identity groups are distinct endpoint attributes in Cisco ISE, the policy's logical profile condition will not be met because the expected logical profile is not assigned, despite the identity group assignment.
Concept tested: Cisco ISE endpoint identity groups vs. logical profiles
Source: https://www.cisco.com/c/en/us/td/docs/security/ise/2-7/admin_guide/b_ISE_admin_guide_27/b_ISE_admin_guide_27_chapter_011.html#concept_35417036495A4017A94D48154D495201
Topics
Community Discussion
No community discussion yet for this question.