
300-715 · Question #204
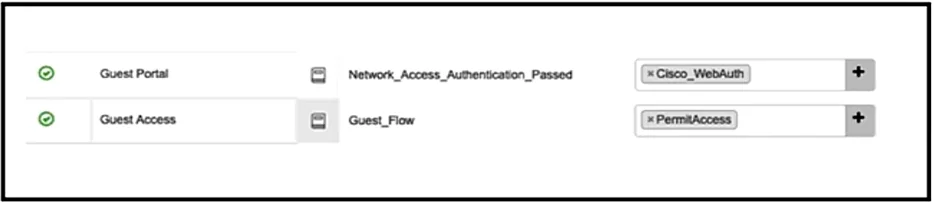
Refer to the exhibit. An engineer is configuring Cisco ISE for guest services and needs any unregistered guests redirected to the guest portal for authentication, then have a CoA provide them full…
The correct answer is A. The Guest_Flow condition is not in the line that gives access to the quest portal. The configuration is failing because the Guest_Flow condition, which identifies endpoints needing redirection, is missing from the authorization rule intended to send guests to the portal.
Question
Refer to the exhibit. An engineer is configuring Cisco ISE for guest services and needs any unregistered guests redirected to the guest portal for authentication, then have a CoA provide them full access to the network segmented via firewalls. Why is the given configuration failing to accomplish this goal?
Exhibit
Options
- AThe Guest_Flow condition is not in the line that gives access to the quest portal
- BThe Network_Access_Authentication_Passed condition will not work with guest services for portal
- CThe Permit Access result is not set to restricted access in its policy line
- DThe Guest Portal and Guest Access policy lines are in the wrong order
How the community answered
(33 responses)- A79% (26)
- B3% (1)
- C12% (4)
- D6% (2)
Why each option
The configuration is failing because the `Guest_Flow` condition, which identifies endpoints needing redirection, is missing from the authorization rule intended to send guests to the portal.
For unregistered guests to be redirected to a guest portal, the authorization rule responsible for the initial redirect must correctly identify them. The absence of an appropriate `Guest_Flow` related condition (e.g., `Session:GuestFlow NOT_EQUALS Guest`) in that policy line prevents the rule from accurately targeting and redirecting unregistered guests to the portal.
The `Network_Access_Authentication_Passed` condition is typically used in the subsequent authorization rule to grant full access after successful portal authentication, so it is necessary for guest services.
The initial 'Permit Access' result for guest redirection is usually restricted access (e.g., a redirect ACL), while full access is granted after portal authentication and CoA, so this choice misunderstands the flow.
While incorrect policy order is a common failure, the specific issue described is a missing condition within the redirect policy line itself, rather than the relative placement of distinct policy lines.
Concept tested: Cisco ISE guest flow authorization conditions
Source: https://www.cisco.com/c/en/us/td/docs/security/ise/2-3/admin_guide/b_ise_admin_guide_23/b_ise_admin_guide_23_chapter_0110.html
Topics
Community Discussion
No community discussion yet for this question.