
300-715 · Question #161
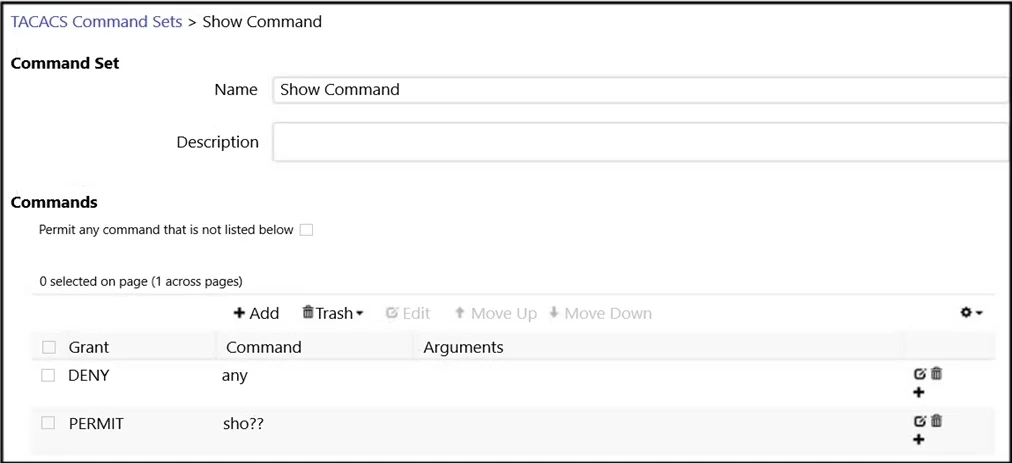
Refer to the exhibit. An engineer is creating a new TACACS+ command set and cannot use any show commands after logging into the device with this command set authorization. Which configuration is…
The correct answer is C. The wildcard command listed is in the wrong format. The issue preventing the use of 'show' commands is caused by an incorrect format in the wildcard command used within the TACACS+ command set definition. TACACS+ command sets require specific regular expression syntax for wildcards.
Question
Refer to the exhibit. An engineer is creating a new TACACS+ command set and cannot use any show commands after logging into the device with this command set authorization. Which configuration is causing this issue?
Exhibit
Options
- AQuestion marks are not allowed as wildcards for command sets.
- BThe command set is allowing all commands that are not in the command list
- CThe wildcard command listed is in the wrong format
- DThe command set is working like an ACL and denying every command.
How the community answered
(34 responses)- A3% (1)
- B9% (3)
- C82% (28)
- D6% (2)
Why each option
The issue preventing the use of 'show' commands is caused by an incorrect format in the wildcard command used within the TACACS+ command set definition. TACACS+ command sets require specific regular expression syntax for wildcards.
Question marks can be used as wildcards in some contexts, but TACACS+ command sets often rely on regular expressions where the syntax for wildcards is more specific, such as `.` for any single character or `.*` for any sequence of characters.
If the command set were allowing all commands not in the list, the user would be able to execute 'show' commands, which contradicts the problem statement that they cannot use them.
TACACS+ command sets often utilize regular expressions for defining command permissions. If the intended wildcard for 'show' commands (e.g., `^show.*`) is syntactically incorrect or uses an unsupported wildcard character, the commands will not match any `permit` rule and will therefore be implicitly denied. This results in the user being unable to execute 'show' commands.
While TACACS+ command sets function like ACLs, denying 'every command' would prevent any action, potentially even login, which is not the specific issue described; the user can log in but cannot use 'show' commands.
Concept tested: TACACS+ Command Set Wildcard Syntax
Source: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_usr_radtac/configuration/xe-16/sec-usr-radtac-xe-16-book/sec-cfg-tac-plus.html
Topics
Community Discussion
No community discussion yet for this question.