
300-715 · Question #144
Drag and Drop Question Drag and drop the description from the left onto the protocol on the right that is used to carry out system authentication, authentication, and accounting. Answer:
The correct answer is encrypts the entire payload; separates authentication and authorization; primary use is device administration; combines authentication and authorization; encrypts only the password field; primary use is network access. The question requires matching descriptions of authentication, authorization, and accounting (AAA) protocols to their respective categories, TACACS+ or RADIUS, based on their key characteristics.
Question
Drag and Drop Question Drag and drop the description from the left onto the protocol on the right that is used to carry out system authentication, authentication, and accounting. Answer:
Exhibit
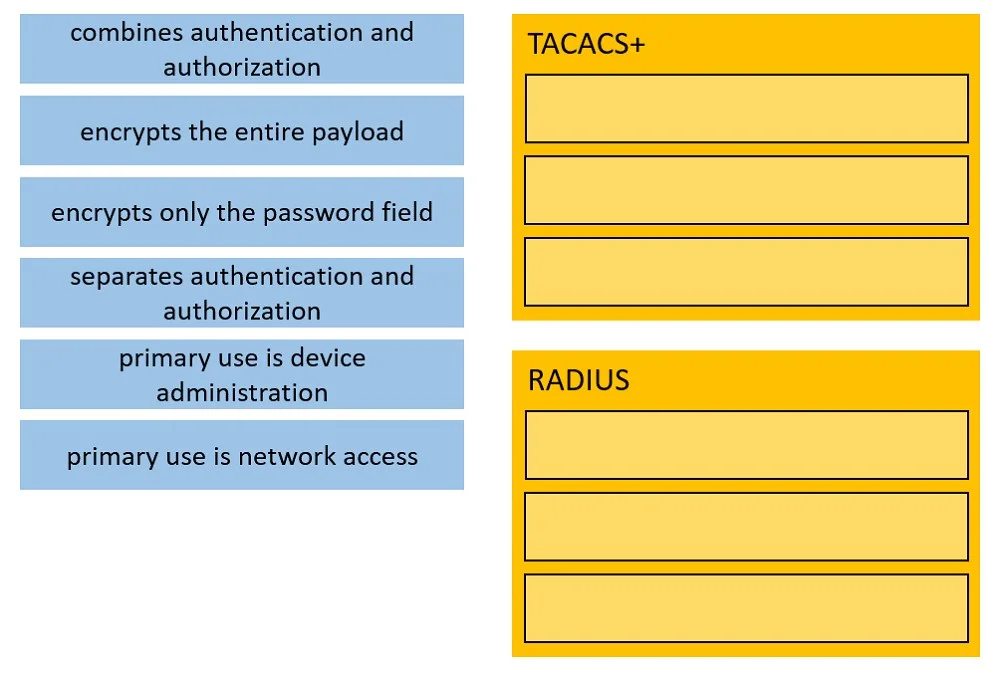
Answer Area
Drag items
Correct arrangement
- encrypts the entire payload
- separates authentication and authorization
- primary use is device administration
- combines authentication and authorization
- encrypts only the password field
- primary use is network access
Explanation
The question requires matching descriptions of authentication, authorization, and accounting (AAA) protocols to their respective categories, TACACS+ or RADIUS, based on their key characteristics.
Approach. The correct interaction involves dragging each description from the left column to the appropriate empty slot under either 'TACACS+' or 'RADIUS' on the right.
For TACACS+:
- 'encrypts the entire payload' - TACACS+ encrypts the entire body of the packet, providing a higher level of security compared to RADIUS.
- 'separates authentication and authorization' - TACACS+ uses a modular design where authentication, authorization, and accounting are handled as distinct processes, allowing for more granular control over authorization.
- 'primary use is device administration' - TACACS+ is commonly used for managing access to network devices like routers, switches, and firewalls due to its robust authorization capabilities.
For RADIUS:
- 'combines authentication and authorization' - RADIUS typically bundles authentication and authorization together within the same packet, making it less flexible in separating these functions.
- 'encrypts only the password field' - RADIUS encrypts only the password in the access-request packet, while the username and other authorization attributes are often sent in plain text (though Transport Layer Security-based implementations exist).
- 'primary use is network access' - RADIUS is widely used for authenticating users for network access services such as Wi-Fi (802.1X), VPNs, dial-up, and DSL.
Common mistakes.
- common_mistake. A common mistake would be to confuse the characteristics of TACACS+ and RADIUS, particularly regarding encryption scope, the separation of AAA functions, and primary use cases. For instance, incorrectly dragging 'encrypts the entire payload' to RADIUS or 'separates authentication and authorization' to RADIUS would be wrong because RADIUS encrypts only the password and combines authentication and authorization. Similarly, assigning 'primary use is network access' to TACACS+ or 'primary use is device administration' to RADIUS would be incorrect, as their primary applications differ significantly based on their design strengths.
Concept tested. The core concept being tested is the understanding of the key differences and characteristics of TACACS+ and RADIUS protocols, which are fundamental AAA (Authentication, Authorization, and Accounting) protocols used in network security.
Topics
Community Discussion
No community discussion yet for this question.