
300-710 · Question #123
Refer to the exhibit. What must be done to fix access to this website while preventing the same communication to all other websites?
The correct answer is D. Create an access control policy rule to allow port 80 to only 172.1.1.50. To allow access to a specific HTTP website (172.1.1.50) while preventing general web access to other sites, an Access Control Policy rule must be created to permit port 80 traffic only to that specific IP address.
Question
Refer to the exhibit. What must be done to fix access to this website while preventing the same communication to all other websites?
Exhibit
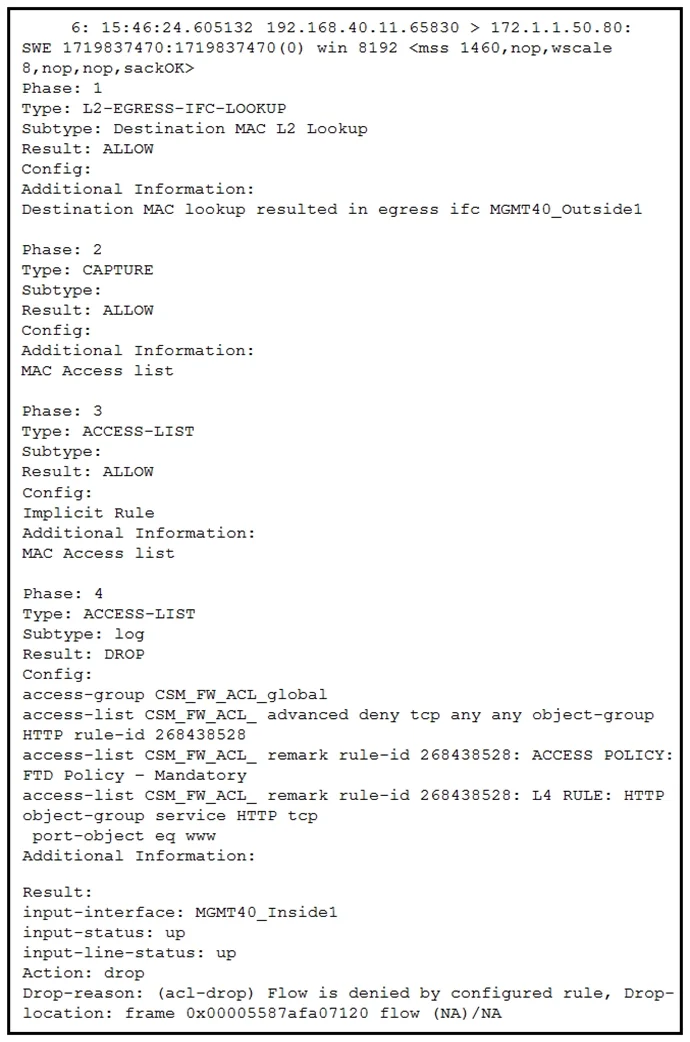
Options
- ACreate an intrusion policy rule to have Snort allow port 80 to only 172.1.1.50.
- BCreate an intrusion policy rule to have Snort allow port 443 to only 172.1.1.50.
- CCreate an access control policy rule to allow port 443 to only 172.1.1.50.
- DCreate an access control policy rule to allow port 80 to only 172.1.1.50.
How the community answered
(56 responses)- A4% (2)
- B18% (10)
- C7% (4)
- D71% (40)
Why each option
To allow access to a specific HTTP website (172.1.1.50) while preventing general web access to other sites, an Access Control Policy rule must be created to permit port 80 traffic only to that specific IP address.
Intrusion policies (Snort) are for detecting and preventing exploits, not for defining basic network access permissions. Snort acts on traffic already allowed by the Access Control Policy.
Intrusion policies do not control basic traffic allowance; this is the function of Access Control Policies. Additionally, HTTPS traffic uses port 443, not 80.
While an Access Control Policy rule is the correct mechanism, if the website is an unencrypted HTTP site, it would utilize port 80, not 443 (which is for HTTPS).
Access Control Policies (ACPs) in Cisco Firepower determine what network traffic is allowed or blocked. By creating an ACP rule specifically to permit HTTP (port 80) traffic to the destination IP address 172.1.1.50 and placing it before any general deny rules, access to that website is restored while other web communication remains blocked.
Concept tested: Cisco Firepower Access Control Policy for web traffic
Source: https://www.cisco.com/c/en/us/td/docs/security/firepower/70/configuration/guide/fpmc-config-guide-70/access_control_policies_and_rules.html
Topics
Community Discussion
No community discussion yet for this question.