
300-710 · Question #119
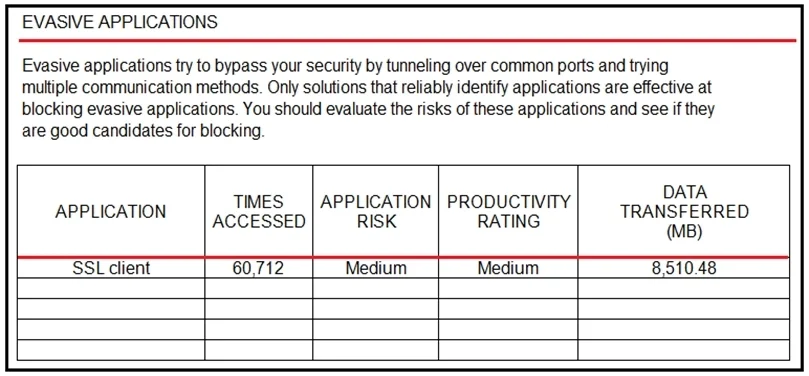
Refer to the exhibit. An administrator is looking at some of the reporting capabilities for Cisco Firepower and noticed this section of the Network Risk report showing a lot of SSL activity that…
The correct answer is A. Use SSL decryption to analyze the packets. SSL/TLS encryption is commonly used as an evasion technique because traditional firewalls and IDS/IPS cannot inspect encrypted payload content. Cisco FTD's SSL Decryption (TLS Inspection) policy allows the appliance to decrypt inbound or outbound SSL/TLS sessions, apply the…
Question
Refer to the exhibit. An administrator is looking at some of the reporting capabilities for Cisco Firepower and noticed this section of the Network Risk report showing a lot of SSL activity that cloud be used for evasion. Which action will mitigate this risk?
Exhibit
Options
- AUse SSL decryption to analyze the packets.
- BUse encrypted traffic analytics to detect attacks
- CUse Cisco AMP for Endpoints to block all SSL connection
- DUse Cisco Tetration to track SSL connections to servers.
How the community answered
(51 responses)- A82% (42)
- B6% (3)
- C10% (5)
- D2% (1)
Explanation
SSL/TLS encryption is commonly used as an evasion technique because traditional firewalls and IDS/IPS cannot inspect encrypted payload content. Cisco FTD's SSL Decryption (TLS Inspection) policy allows the appliance to decrypt inbound or outbound SSL/TLS sessions, apply the full suite of deep packet inspection, intrusion detection, file analysis, and application control to the decrypted content, and then re-encrypt the traffic before forwarding. This eliminates the blind spot created by encryption. Encrypted Traffic Analytics (option B) provides some behavioral detection without decryption but is far less comprehensive. Cisco AMP for Endpoints (option C) operates at the host level, not the network flow. Cisco Tetration (option D) is a workload security tool, not suited for this use case.
Topics
Community Discussion
No community discussion yet for this question.