
Cisco
300-620 · Question #78
An engineer must limit management access to me Cisco ACI fabric that originates from a single subnet where the NOC operates. Access should be limited to SSH and HTTPS only. Where should the policy…
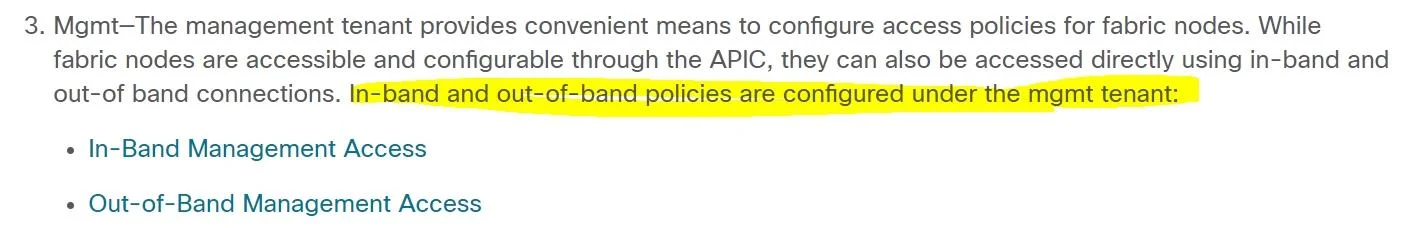
The correct answer is A. policy in the management tenant. x/Operating_ACI/guide/b_Cisco_Operating_ACI/b_Cisco_Operating_ACI_chapter_0111.ht ml
ACI Management
Question
An engineer must limit management access to me Cisco ACI fabric that originates from a single subnet where the NOC operates. Access should be limited to SSH and HTTPS only. Where should the policy be configured on the Cisco APIC to meet the requirements?
Exhibit
Options
- Apolicy in the management tenant
- Bpolicy on the management VLAN
- CACL on the management interface of the APIC
- DACL on the console interface
How the community answered
(37 responses)- A76% (28)
- B3% (1)
- C8% (3)
- D14% (5)
Explanation
x/Operating_ACI/guide/b_Cisco_Operating_ACI/b_Cisco_Operating_ACI_chapter_0111.ht ml
Topics
#management access#security policy#management tenant#SSH/HTTPS
Community Discussion
No community discussion yet for this question.