
300-215 · Question #95
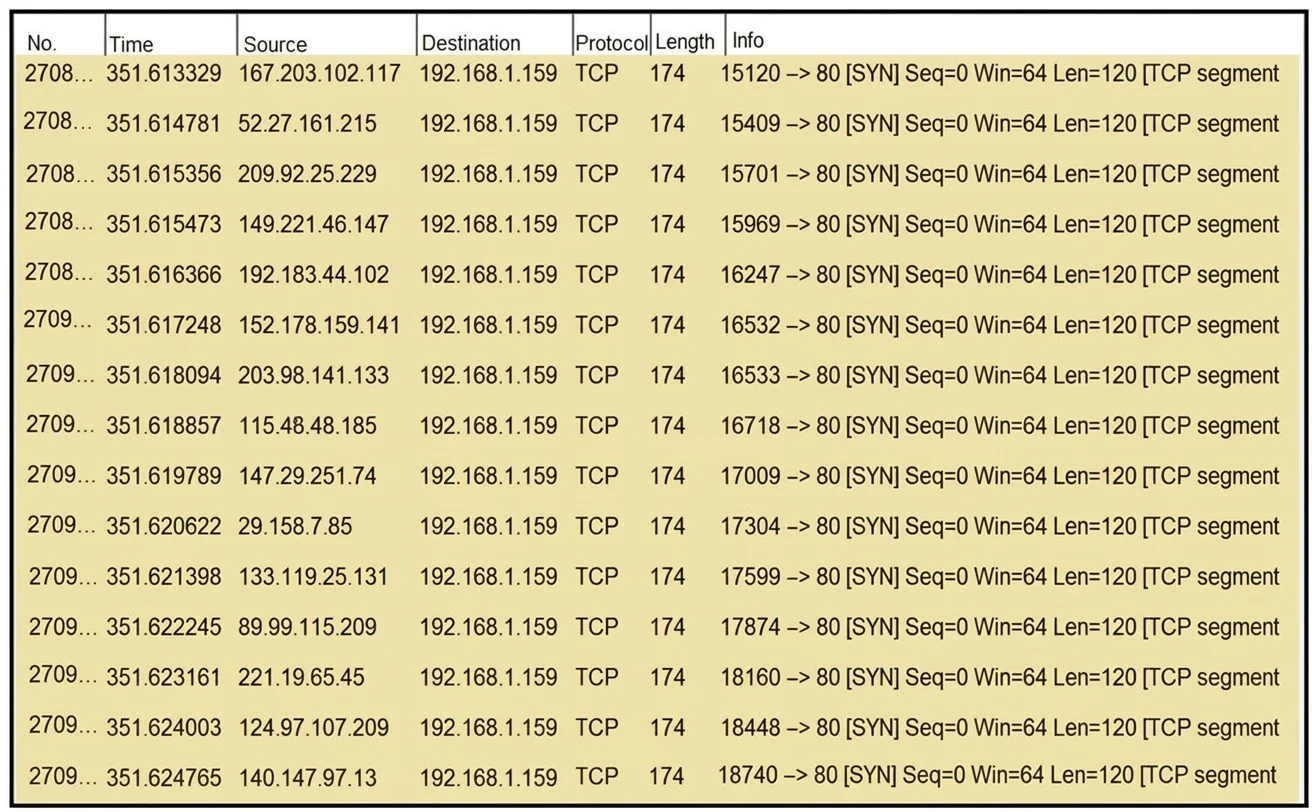
Refer to the exhibit. What should an engineer determine from this Wireshark capture of suspicious network traffic?
The correct answer is A. There are signs of SYN flood attack, and the engineer should increase the backlog and recycle. In the provided Wireshark capture, we see multiple TCP SYN packets being sent from different source IP addresses to the same destination IP address (192.168.1.159:80) within a short time window. These SYN packets do not show a corresponding SYN-ACK or ACK response, indicating…
Question
Refer to the exhibit. What should an engineer determine from this Wireshark capture of suspicious network traffic?
Exhibit
Options
- AThere are signs of SYN flood attack, and the engineer should increase the backlog and recycle
- BThere are signs of a malformed packet attack, and the engineer should limit the packet size and
- CThere are signs of a DNS attack, and the engineer should hide the BIND version and restrict zone
- DThere are signs of ARP spoofing, and the engineer should use Static ARP entries and IP
How the community answered
(61 responses)- A67% (41)
- B21% (13)
- C3% (2)
- D8% (5)
Explanation
In the provided Wireshark capture, we see multiple TCP SYN packets being sent from different source IP addresses to the same destination IP address (192.168.1.159:80) within a short time window. These SYN packets do not show a corresponding SYN-ACK or ACK response, indicating that these TCP connection requests are not being completed. This pattern is indicative of a SYN flood attack, a type of Denial of Service (DoS) attack. In this attack, a malicious actor floods the target system with a high volume of TCP SYN requests, leaving the target's TCP connection queue (backlog) filled with half-open connections. This can exhaust system resources, causing legitimate connection requests to be denied or delayed. Increasing the backlog queue: This allows the server to hold more half-open connections. Recycling the oldest half-open connections: This ensures that legitimate connections have a chance to be established if the backlog fills up.
Topics
Community Discussion
No community discussion yet for this question.