
300-215 · Question #109
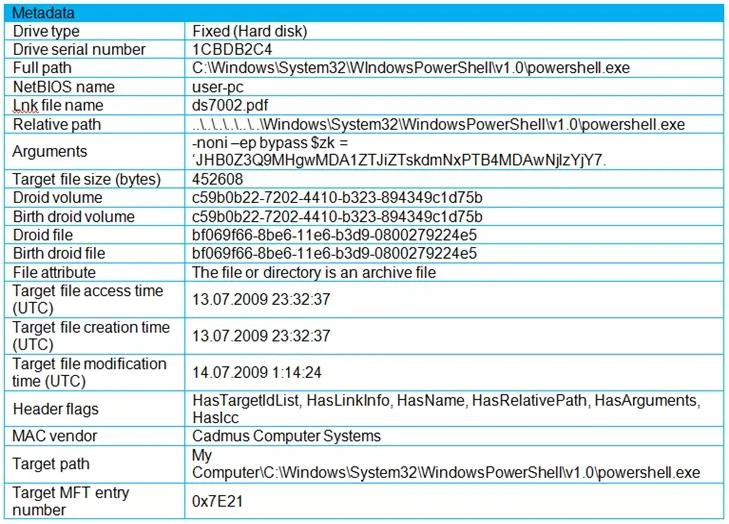
Refer to the exhibit. An engineer is analyzing a .LNK (shortcut) file recently received as an email attachment and blocked by email security as suspicious. What is the next step an engineer should…
The correct answer is D. Open the file in a sandbox environment for further behavioral analysis as the file contains a. The metadata in the exhibit reveals a strong indicator that this .LNK file (shortcut) is malicious: The shortcut file is named "ds7002.pdf" but actually points to the execution of PowerShell: Full path: C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe Arguments…
Question
Refer to the exhibit. An engineer is analyzing a .LNK (shortcut) file recently received as an email attachment and blocked by email security as suspicious. What is the next step an engineer should take?
Exhibit
Options
- ADelete the suspicious email with the attachment as the file is a shortcut extension and does not
- BUpload the file to a virus checking engine to compare with well-known viruses as the file is a virus
- CQuarantine the file within the endpoint antivirus solution as the file is a ransomware which will
- DOpen the file in a sandbox environment for further behavioral analysis as the file contains a
How the community answered
(51 responses)- A2% (1)
- B4% (2)
- C10% (5)
- D84% (43)
Explanation
The metadata in the exhibit reveals a strong indicator that this .LNK file (shortcut) is malicious: The shortcut file is named "ds7002.pdf" but actually points to the execution of PowerShell: Full path: C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe Arguments include: -noni -ep bypass $z = '...'; indicating an attempt to run a PowerShell script with execution policy bypassed (a known tactic for fileless malware delivery). The file is masked as a PDF (common social engineering technique), and PowerShell execution via .LNK is a signature technique used by many malware families to initiate second-stage payloads or scripts. Given this, the correct and safest course of action is to: Open the .LNK file in a sandbox environment (D). This enables safe behavioral analysis to observe what actions it attempts upon execution without endangering live systems.
Topics
Community Discussion
No community discussion yet for this question.