
300-170 · Question #166
Refer to the exhibit. You are reinstalling Core-02 by using POAP. What do you configure on the vPC to prevent traffic from being sent to Core-02 while Core-02 comes online?
The correct answer is A. LACP on the vPC peer link. This question focuses on how to prevent traffic from being sent to a vPC peer undergoing POAP, requiring control over the vPC peer link's operational state.
Question
Refer to the exhibit. You are reinstalling Core-02 by using POAP. What do you configure on the vPC to prevent traffic from being sent to Core-02 while Core-02 comes online?
Exhibit
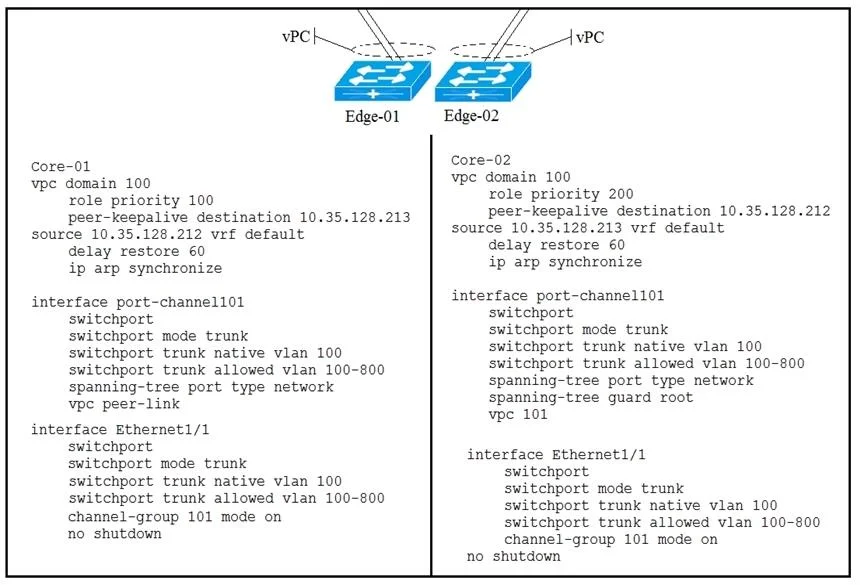
Options
- ALACP on the vPC peer link
- BLLDP on the vPC links
- CLACP on the vPC links
- Dpeer gateway in the vPC domain
How the community answered
(40 responses)- A73% (29)
- B15% (6)
- C3% (1)
- D10% (4)
Why each option
This question focuses on how to prevent traffic from being sent to a vPC peer undergoing POAP, requiring control over the vPC peer link's operational state.
Configuring LACP on the vPC peer link is crucial for controlling its operational state. By leveraging LACP's capabilities, such as `lacp suspend-individual` or ensuring the peer link's LACP state is not fully established until Core-02 is fully provisioned, the peer link can be prevented from coming up. When the vPC peer link is down or suspended, the secondary vPC peer (Core-02) will block traffic on its vPC member ports, effectively preventing it from receiving traffic during POAP.
LLDP (Link Layer Discovery Protocol) is a discovery protocol used for exchanging device information between neighbors, but it does not control traffic forwarding or the operational state of vPC links to prevent traffic.
Configuring LACP on the vPC links (member ports) is essential for the vPC to aggregate client traffic, but this does not specifically prevent traffic from being sent to Core-02 during POAP without affecting the other vPC peer's connectivity.
Peer gateway is a vPC feature that allows vPC peers to act as a single gateway for connected devices, primarily optimizing ARP and routing, but it does not prevent traffic forwarding to a switch undergoing initial provisioning via POAP.
Concept tested: vPC LACP peer link traffic control
Source: https://www.cisco.com/c/en/us/td/docs/dcn/nx-os/nexus9000/102x/configuration/interfaces/cisco-nexus-9000-series-nx-os-interfaces-configuration-guide-102x/m-vpc.html
Topics
Community Discussion
No community discussion yet for this question.