
200-201 · Question #310
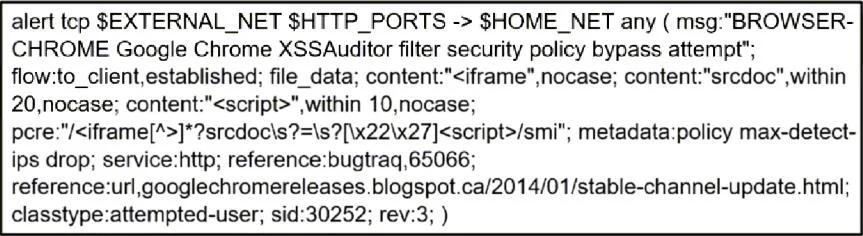
Refer to the exhibit. A company's user HTTP connection to a malicious site was blocked according to configured policy. What is the source technology used for this measure?
The correct answer is C. IPS. The exhibit shows a rule written in the format used by intrusion detection and prevention systems like Snort or Suricata. The rule uses keywords such as alert, sid (signature ID), and classtype, which are characteristic of IPS/IDS signatures. The rule is designed to detect and…
Question
Refer to the exhibit. A company's user HTTP connection to a malicious site was blocked according to configured policy. What is the source technology used for this measure?
Exhibit
Options
- Anetwork application control
- Bfirewall
- CIPS
- Dweb proxy
How the community answered
(32 responses)- A3% (1)
- B6% (2)
- C91% (29)
Explanation
The exhibit shows a rule written in the format used by intrusion detection and prevention systems like Snort or Suricata. The rule uses keywords such as alert, sid (signature ID), and classtype, which are characteristic of IPS/IDS signatures. The rule is designed to detect and block specific attack patterns in HTTP traffic (in this case, a Chrome XSSAuditor bypass attempt). The drop action in the metadata and the detailed pattern matching are typical of IPS functionality, which can actively block malicious traffic.
Topics
Community Discussion
No community discussion yet for this question.